The Definitive Digital Guardian: The Security Operations Center (SOC) Market Solution
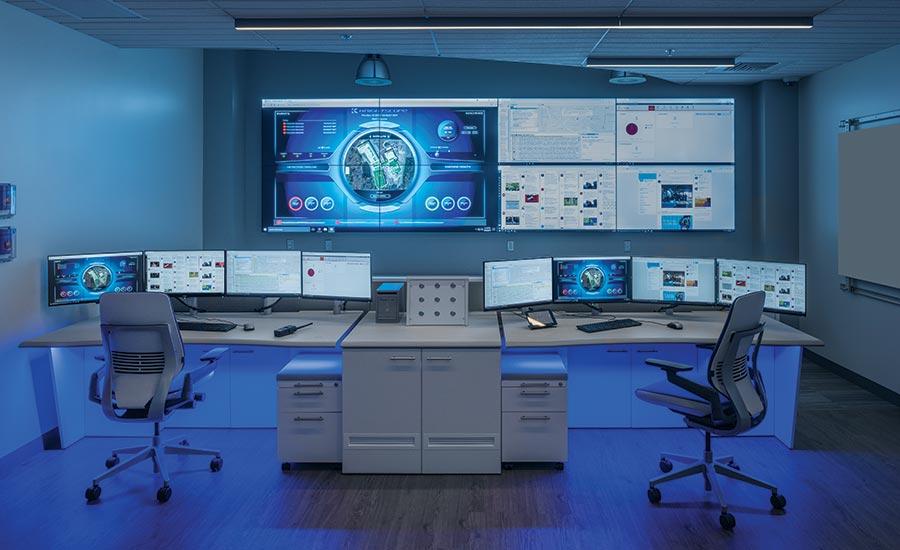
The Essential Solution for 24/7 Threat Visibility and Detection
In today's digital world, cyber-attacks do not adhere to business hours. A threat can emerge at any time, from anywhere in the world. The most fundamental problem that the Security Operations Center (SOC) Market Solution addresses is providing continuous, around-the-clock visibility and threat detection. A SOC is the solution that ensures that there are always "eyes on glass," monitoring the organization's digital estate for signs of malicious activity. It provides a centralized solution for collecting and analyzing security data from across the entire enterprise—from firewalls and servers to endpoints and cloud services. By using advanced technologies like SIEM and behavioral analytics, the SOC can correlate disparate events and identify the subtle patterns that indicate a sophisticated attack is underway. This constant vigilance is the solution that dramatically shortens the "time to detect," which is a critical factor in minimizing the impact of a security breach. Without a 24/7 SOC, an organization is effectively blind to attacks that occur overnight or on weekends, leaving them exposed for hours or even days.
A Solution for Rapid Incident Response and Containment
Detecting a threat is only half the battle; the speed and effectiveness of the response are what ultimately determine the outcome of a security incident. A SOC provides a structured and rapid solution for incident response and containment. When a threat is detected, the SOC's well-defined processes and playbooks are immediately activated. The SOC analysts provide the solution by quickly investigating the alert, confirming its validity, and assessing its potential impact. They then coordinate the response actions needed to contain the threat and prevent it from spreading. This might involve isolating a compromised laptop from the network, blocking a malicious IP address at the firewall, or disabling a compromised user account. The SOC acts as the central command and control for the entire incident response effort, ensuring that all actions are coordinated and effective. This ability to respond in a matter of minutes, rather than hours or days, is a powerful solution that can be the difference between a minor security event and a catastrophic, business-crippling data breach.
A Solution for Addressing the Cybersecurity Skills Gap
A major challenge facing almost every organization is the severe global shortage of skilled cybersecurity professionals. Hiring and retaining the talent needed to build and operate an effective internal security team is incredibly difficult and expensive. The outsourced SOC model—either through a traditional MSSP or a modern MDR provider—offers a powerful solution to this skills gap problem. By partnering with a SOC provider, an organization gains immediate access to a large team of highly skilled and experienced security analysts, threat hunters, and incident responders. This is a solution that allows a small or medium-sized business to leverage the same level of expertise as a Fortune 500 company, without having to bear the full cost and administrative burden of hiring them directly. The SOC provider takes on the responsibility for recruiting, training, and retaining the talent, and for providing 24/7 coverage. For the vast majority of businesses, this outsourced model is the most practical and cost-effective solution for obtaining the advanced security capabilities they need to defend themselves.
A Solution for Demonstrating Compliance and Due Diligence
In an environment of increasing regulatory scrutiny, organizations are under constant pressure to demonstrate that they are taking their data protection responsibilities seriously. A SOC provides a clear and tangible solution for meeting these compliance and due diligence requirements. The logs and reports generated by the SOC's SIEM platform provide a detailed, auditable record of all security monitoring activities, which can be presented to auditors or regulators as evidence of a robust security program. The SOC's ability to rapidly detect and respond to incidents is a key part of complying with the strict breach notification timelines mandated by laws like GDPR. By having a SOC—whether in-house or outsourced—an organization can demonstrate to its board, its customers, its insurers, and its regulators that it is not being negligent. It is a solution that shows the company is proactively managing its cybersecurity risk in a structured and professional manner. This not only helps to avoid regulatory fines but also builds trust and confidence with all key stakeholders, which is an invaluable asset in today's market.
➤ Latest Market Intelligence from Market Research Future:

 English
 Arabic
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek